
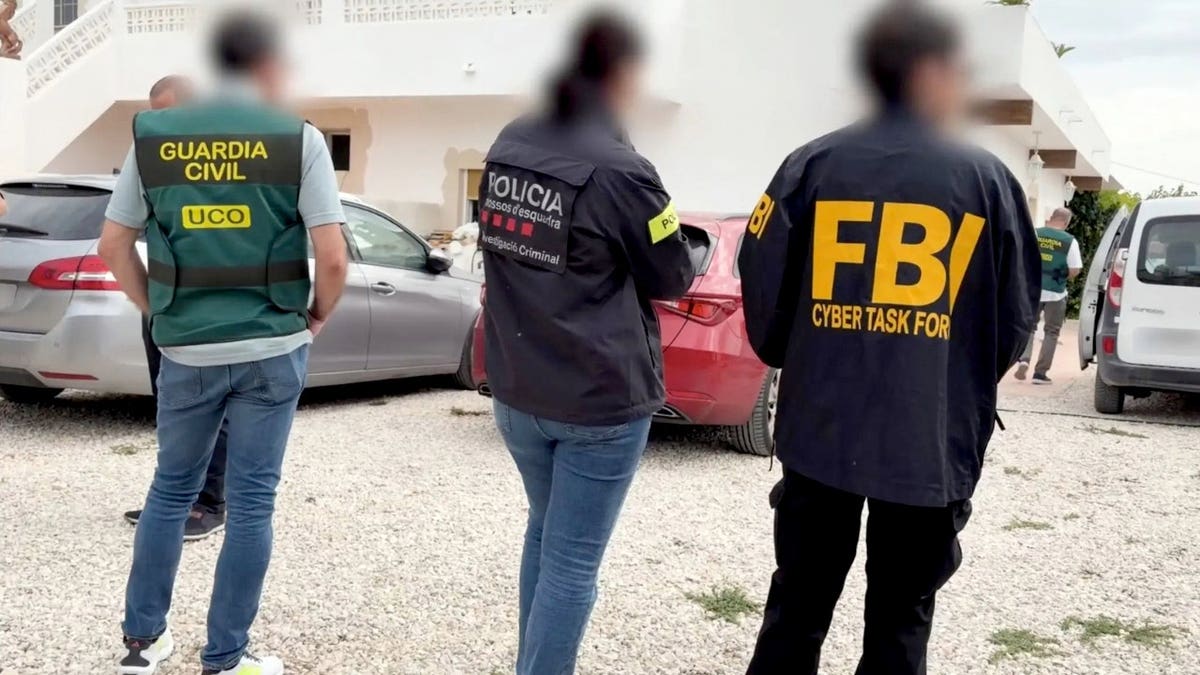
Fox News has reported that a 16-year-old is suspected of being a primary operator for KillSec, an international ransomware group. This group is linked to around 1,000 attacks globally, with about 500 confirmed successful. Authorities have dismantled KillSec’s operations, seizing their servers and leak site, as well as securing 110 terabytes of potentially compromised data.
Investigative Breakthrough and Arrests
An extensive international investigation culminated in the takedown known as Operation KillSwitch on September 30. The FBI, along with law enforcement agencies from the US, and several European nations, including Europol and Eurojust, coordinated efforts. Authorities conducted searches in Greece, Romania, Spain, and the UK, arresting three suspects and seizing five central servers tied to KillSec.
The investigation uncovered that the alleged main operator and administrator of KillSec is a teenager. Another member, recently turned 18, was identified as a developer. Some group affiliates were detected, and investigations are ongoing. KillSec had been operating since roughly 2024, targeting organizations by exploiting vulnerabilities in software and systems. They extracted internal sensitive data and used it as leverage.
The Ransomware Tactics
KillSec utilized threat tactics typical of ransomware groups. They listed victim organizations on a dark web site, threatening to release stolen data if ransom demands were not met. Reports indicate that crucial data was sometimes made public when ransoms weren’t paid. Ransom payments significantly enhanced the group’s operations, signaling a shift in ransomware methodology where the data itself, and not just system locks, become the bargaining chip.
Moreover, investigators noted that KillSec incorporated artificial intelligence in building ransomware infrastructure and selecting targets. AI usage doesn’t imply fully autonomous attacks, but it highlights how technology assists even young perpetrators in complex cybercrimes.
Preventative Measures Against Ransomware
The recent crackdown teaches vital lessons applicable to everyone, beyond organizations. Ransomware often exploits similar vulnerabilities, reinforcing the importance of basic security practices. Here are seven ways to minimize ransomware risks:
- Install Updates: Maintain updated software and security systems across all devices to patch known vulnerabilities.
- Use Strong Passwords: Avoid using the same password for multiple accounts. Utilize a password manager to handle unique, robust credentials.
- Enable Two-Factor Authentication: Apply additional verification steps on crucial accounts to bolster security.
- Keep Offline Backups: Store important files on external drives disconnected post-backup to prevent ransomware from accessing them.
- Be Wary of Downloads: Approach unanticipated emails, downloads, or updates with caution to avoid inadvertently inviting threats.
- Use Security Software: Deploy antivirus and security programs to detect potential threats and maintain vigilance over device performance.
- Ransomware Response: In case of a ransomware attack, disconnect infected devices from the network, and refrain from connecting backup drives. Report the incident to law enforcement promptly.
This incident emphasizes the evolving nature of cybercrime and the necessity for ongoing vigilance. Even if not directly affected, understanding and employing basic security practices make devices less susceptible to attacks.